❌

Reading view

Presentation: Fixing the AI Infra Scale Problem by Stuffing 1M Sandboxes in a Single Server
Felipe Huici explains how Unikraft achieves millisecond cold boots, stateful scale-to-zero, and extreme density for sandboxing AI workloads. He discusses isolation primitives, Linux kernel optimizations, and snapshotting tricks, demonstrating how to maintain sub-10ms performance at scale while integrating seamlessly into Kubernetes environments with hardware-level security.

By Felipe Huici
  •  

Azure Virtual Desktop Hybrid Reaches GA with Licensing Details Unpublished

Microsoft has made Azure Virtual Desktop Hybrid generally available. Session hosts run on customer hardware through Azure Arc while brokering stays in Azure. The Hybrid service license is unpriced, Windows Server support requires RDS CALs with Software Assurance, and multi-session Windows is not supported at all.

By Steef-Jan Wiggers
  •  

HashiCorp Packer 1.16 Adds Native SLSA Provenance Generation and Verification for Machine Images

HashiCorp has released Packer v1.16.0, adding native support for generating, signing, and verifying SLSA provenance attestations for every image the tool builds. The release provides teams with a secure, tamper-proof record of how a machine image was made. It does this without needing extra supply-chain tools.

By Claudio Masolo
  •  

Presentation: Platform Engineering in the Age of AI

The panelists explain how platform teams adapt to support AI-assisted engineering, highlighting which capabilities belong in the platform. They discuss trade-offs between standardization and developer autonomy, while sharing strategies to manage AI tooling, security guardrails, and shifting workflows.

By StΓ©phane Di Cesare, Davide de Paolis, Stephen Cihak, Camila Macedo, Renato Losio
  •  

GitLab Warns That AI Agent Sandboxes Are Only as Secure as Their Network Access

GitLab warns that isolating an AI coding agent in a sandbox does not necessarily make the agent safe. In a new security analysis, the company describes an internal evaluation in which an AI agent escaped its sandbox by exploiting a vulnerable package proxy that had been explicitly placed on the sandbox's allowlist.

By Craig Risi
  •  

Article: Implementing Chaos Engineering in Financial Payment Systems: Lessons from Enterprise ECS Deployments

Standard chaos engineering assumes experiments stop cleanly, blast radius is knowable in advance, and production is fair game. Payment systems violate all three. Salim Adedeji describes ECS-specific failure modes from enterprise deployments: a 60-second DNS TTL that produced 93-second failover, retry logic amplifying database load 2.4x, and AZ rebalancing loops that generic tooling misses.

By Salim Adedeji
  •  

Does ICANN Open the Door on Identity Theft by Dropping 3rd Level .name Domains Registrations?

Neil Fraser's disclosure highlights a regulatory change affecting the .name top-level domain. Following ICANN's approval, Verisign will eliminate third-level registrations due to declining usage. This affects about 22,000 registrants and raises security concerns, as released second-level domains could be exploited. Affected users are considering legal options to challenge the decision.

By Olimpiu Pop
  •  

Netflix Moves toward Open Source Flink Autoscaler for 30,000+ Streaming Jobs

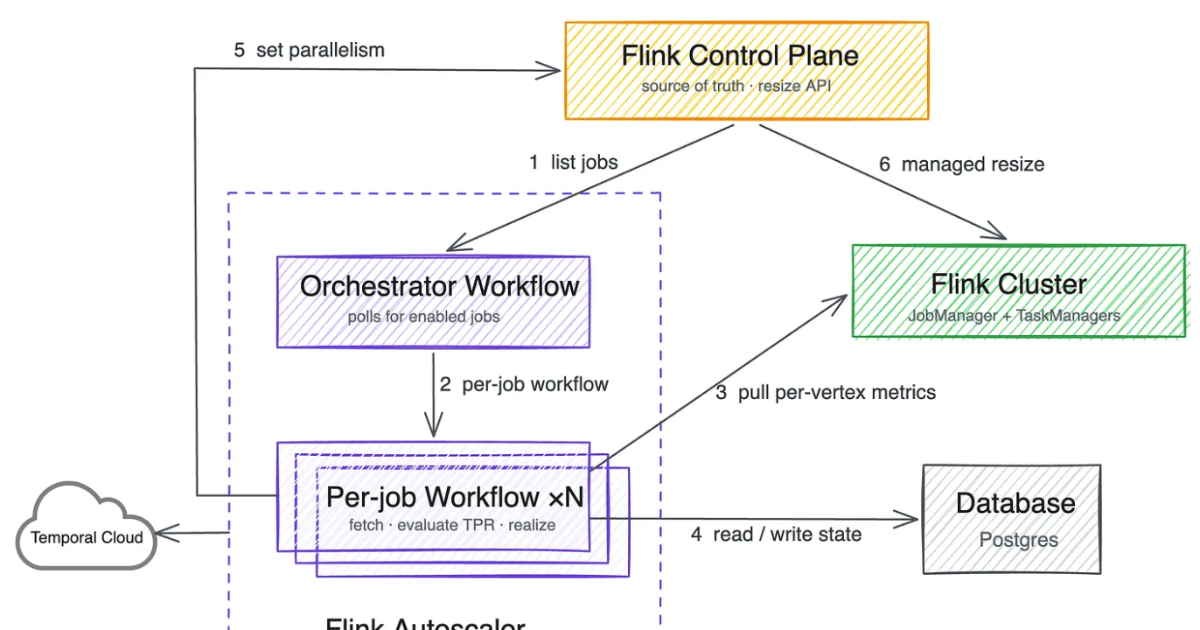
Netflix is moving toward the open-source Apache Flink Autoscaler for more than 30,000 streaming jobs across multiple AWS regions. The operator-level approach addresses limitations of Netflix’s cluster level autoscaler for complex, stateful pipelines. Netflix reports a 58% reduction in annualized Flink compute expenditure for one team, saving approximately $1.1 million annually.

By Leela Kumili
  •  

Zone Redundancy Comes to API Management Standard v2

Microsoft has enabled zone redundancy on the Standard v2 tier of Azure API Management, following its arrival on Premium v2 in December. Standard v2 starts at $700 per month against $2,801 for Premium v2, but carries a 99.95% SLA rather than 99.99%. Zone redundancy can only be configured when creating an instance.

By Steef-Jan Wiggers
  •  

CERN Renounces RHEL in Favor of Debian for its Accelerator Controls Infrastructure

CERN engineers announced a shift from Red Hat-based distributions to Debian for its accelerator control systems. This decision stems from Red Hat's tightening compiler mandates, which threatened legacy hardware. The transition, focused on 2,200 specialized control machines, is set for completion in late 2026, while CERN's other systems will remain with Red Hat and AlmaLinux.

By Olimpiu Pop
  •  
❌